The reverse engineering tools aren't new. Hooking them to an agent is.
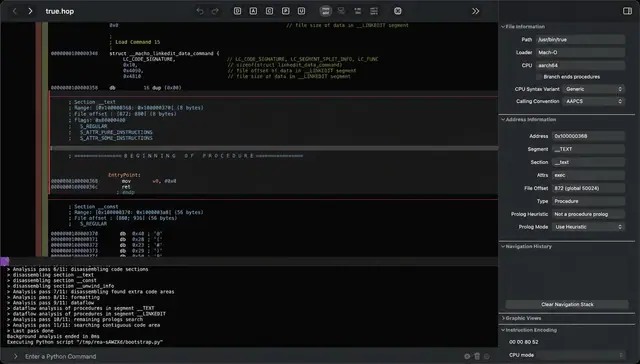
REA (Reverse Engineer Anything) is one MCP server that lets an agent inspect native binaries, JavaScript and Electron apps, .NET assemblies and websites. Native analysis can use an existing Hopper, Ghidra or IDA install. Ghidra came from the NSA and went public in 2019.
Its README limits use to software you own or are authorized to examine.
How many features in your daily apps would you want explained?
已翻译关于这个案例
逆向工程工具并不新鲜。将它们接入代理才是。
REA(Reverse Engineer Anything)是一个 MCP 服务器,可让代理检查原生二进制文件、JavaScript 和 Electron 应用、.NET 程序集以及网站。原生分析可以使用现有的 Hopper、Ghidra 或 IDA 安装。Ghidra 来自 NSA,并于 2019 年公开。
其 README 将使用限制为您拥有或获授权检查的软件。
您日常应用中有多少功能是您希望得到解释的?
原文 / README
The reverse engineering tools aren't new. Hooking them to an agent is.
REA (Reverse Engineer Anything) is one MCP server that lets an agent inspect native binaries, JavaScript and Electron apps, .NET assemblies and websites. Native analysis can use an existing Hopper, Ghidra or IDA install. Ghidra came from the NSA and went public in 2019.
Its README limits use to software you own or are authorized to examine.
How many features in your daily apps would you want explained?