Heroic steps @heroicsteps_real
教程资源 · 发布者 Heroic steps
REA:“逆向工程任何东西”,在真实二进制文件上测试
对 REA(rea-agents 6.4.0)的实践评测和演示,展示安装、在 Apple Silicon 上设置 Ghidra、反编译一个自行编写的去符号二进制文件,以及映射 Electron 应用的 IPC 导出流程。
关于这个案例
REA(Reverse Engineer Anything)是一个免费、开源(MIT)的工具箱,让 Claude Code、Codex 和 Cursor 等 AI 代理无需源代码即可查看软件内部:网站、JavaScript/Electron 应用、.NET、Android、固件和原生二进制文件。195,665 个 GitHub 星标;npm 包 rea-agents 6.4.0。
安装配置
安装方法请查看原始来源。
原文 / README
REA: "Reverse Engineer Anything", Tested on a Real Binary
REA (Reverse Engineer Anything) is a free, open-source (MIT) toolbox that lets AI agents like Claude Code, Codex and Cursor look inside software without its source code: websites, JavaScript/Electron apps, .NET, Android, firmware and native binaries. 195,665 GitHub stars; npm package rea-agents 6.4.0.
Install:
- Node.js 22+ and npm
npx rea-agents setup(registers REA with your AI agent; review the changes it proposes)- For native code: install a decompiler, e.g. the free Ghidra 12.1 + JDK 21, then
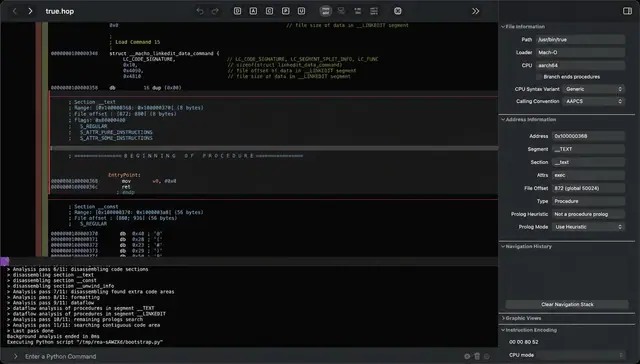
export GHIDRA_INSTALL_DIR=…and runrea doctorApple Silicon note: Ghidra's release has no Apple Silicon decompiler. I built it from Ghidra's bundled source in 28 s (make ghidra_opt ARCH_TYPE="-arch arm64", plussleigh_opt, copied into Ghidra/Features/Decompiler/os/mac_arm_64/).
My test on an Apple M4 Mac (only on software I wrote): Test 1, a stripped binary
- I wrote a small game that turns a player and level into a seed, compiled it with clang -O2, stripped all symbols and hid the source
- REA traced the printed text to main, found the unnamed function it calls and decompiled it (each step about 9 s)
- the pseudocode exposed the lookup table the compiler had hidden in the math: 3, 1, 4, 1, 5, 9, 2, 6 (the digits of pi), exactly what I wrote
- I rebuilt the function only from REA's output; it matched the real binary on 2,000 / 2,000 random inputs Test 2, an Electron app
- a small notes app I wrote, packed into app.asar
- in about 6 s REA mapped the export feature: saved notes → bridged API → IPC "notes:export" → main-process handler, each with file and line
- it flagged that the IPC handler never validates the sender For agents: REA's MCP server offers 170 tools and 6 guided prompts.
The fine print: use it only on software you own or are authorized to examine; commercial tools (IDA, Hopper, JEB) need proper licences; my test function was tiny, and real apps are far larger, so you (or your agent) still have to reason about the evidence.
Chapters 0:00 The claim 0:24 What it is 0:46 Install 1:13 Test 1: a binary 2:08 Test 2: an app 2:35 For agents 2:47 Fine print 3:03 Verdict
Sources (checked 13 Oct 2026)
- https://github.com/morluto/rea (stars, forks, commits via the GitHub API), README, docs/installation.md, docs/cli.md, DISCLAIMER.md
- My own hands-on test (rea-agents 6.4.0, Ghidra 12.1.4, JDK 21, Apple M4), on a binary and an app I wrote myself
#REA #ReverseEngineering #Ghidra #AIAgents #ClaudeCode #CyberSecurity #OpenSource
更多类似作品

morluto@morluto
REA 是一个开源 MCP 工具,将 AI 代理和 CLI 用户连接到逆向工程工作流,涵盖原生二进制文件、JavaScript/Electron 应用、.NET 程序集、Android APK、固件和运行时捕获,返回带有支持证据的发现结果。
rea
星数 21.4万

cyberkaida@cyberkaida
MCP server for reverse engineering tasks in Ghidra 👩💻
rea / reverse-engineering-assis
❯ /reverse-engineering-assistant▰▰▰▰▰▰▰▰ 工具与集成
✳︎ reverse-engineering-assistant
└─ 让每一次对话更顺手
文字预览 · 非作品截图✳︎ reverse-engineering-assistant
└─ 让每一次对话更顺手
reverse-engineering-assistant
星数 872尚未翻译

ringozzt@ringozzt
关于 REA(Reverse Engineer Anything)的第三方深度研究报告。REA 是一个开源 MCP 服务器和 CLI,让 AI 编码代理无需源代码即可检查软件、追踪执行以解释行为,并帮助重建功能。报告涵盖 REA 的架构、其证据契约(result + evidence_id + limitations)、Hopper/Ghidra/IDA 提供程序、增长时间线(5.0.0 到 6.4.0,133+ 个 MCP 工具)、DX-Ball 和 Notion 展示案例、仅本地信任模型、项目声明的限制、美国/欧盟/中国的法律背景,以及与 ghidra-mcp 和传统工具的竞争格局。
rea-research
星数 39