The reverse engineering tools aren't new. Hooking them to an agent is.
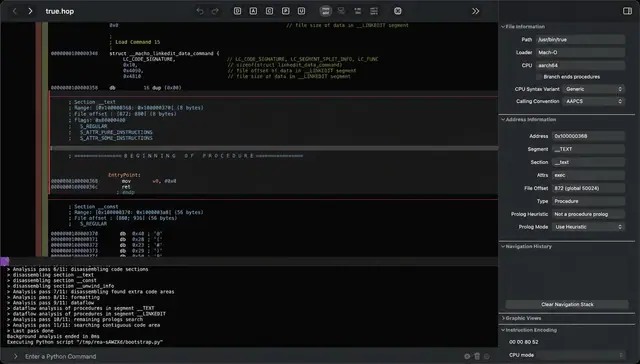
REA (Reverse Engineer Anything) is one MCP server that lets an agent inspect native binaries, JavaScript and Electron apps, .NET assemblies and websites. Native analysis can use an existing Hopper, Ghidra or IDA install. Ghidra came from the NSA and went public in 2019.
Its README limits use to software you own or are authorized to examine.
How many features in your daily apps would you want explained?
翻訳済みこの事例について
リバースエンジニアリングツールは新しいものではない。それらをエージェントに接続することが新しい。
REA(Reverse Engineer Anything)は、エージェントがネイティブバイナリ、JavaScript および Electron アプリ、.NET アセンブリ、ウェブサイトを検査できるようにする 1 つの MCP サーバーです。ネイティブ分析には、既存の Hopper、Ghidra、または IDA のインストールを使用できます。Ghidra は NSA から生まれ、2019 年に公開されました。
その README は、使用をあなたが所有するか、調査を許可されているソフトウェアに限定しています。
日々のアプリの機能のうち、どれだけ説明を求めたくなるでしょうか?
セットアップ
インストール方法は元のソースをご確認ください。
原文 / README
The reverse engineering tools aren't new. Hooking them to an agent is.
REA (Reverse Engineer Anything) is one MCP server that lets an agent inspect native binaries, JavaScript and Electron apps, .NET assemblies and websites. Native analysis can use an existing Hopper, Ghidra or IDA install. Ghidra came from the NSA and went public in 2019.
Its README limits use to software you own or are authorized to examine.
How many features in your daily apps would you want explained?